Tuesday, January 31, 2012

half-assed recovery

from here

inspired by a usenet thread (remember those?)

mindlessly restoring drive images is kind of like hanging the target back up after the attacker knocked it down.

congrats on helping to kill SOPA

from here

i actually played around with the idea of making this site go dark, but decided that somebody needed to help highlight the fact that there is a bigger picture than just SOPA itself. it's been suggested that there are a variety of different adversaries that people face online (and off), and unfortunately their own government (or for most of us in the case of SOPA, a foreign government) is one of them.

Monday, January 30, 2012

war on the unusual

from here (image source one, two, and three)

the TSA are apparently not the brightest bulbs in the chandelier. they really did mistake an insulin pump for a gun. someone turn on a light for these guys.

failure is always on the list

from here

the problem with the checklist is that it promotes the idea of following a simple sequence of steps rather than taking a more comprehensive approach. simple approaches often have simple ways to bypass.

Friday, January 27, 2012

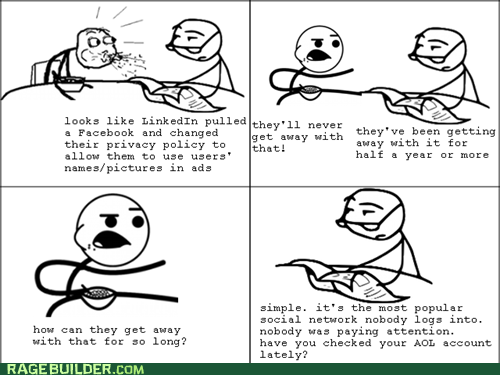
privacy decay

from here

inspired by bob rudis' tweet about the linkedin change

pwnAnywhere

poor symantec. that source code leak from before may not have had any impact on it's anti-virus product yet, but apparently anonymous has found ways of exploiting pcAnywhere and symantec is warning people to stop using it.

(unaltered image source)

Thursday, January 26, 2012

privacy policy beta

this is in recognition of google's recent move to revise their privacy policies and the fact that they will likely piss people off and have to revise them again (and again). google gets away with a lot when they slap the word beta on things, though, so perhaps that's what they should do this time.


(source image)

Wednesday, January 25, 2012

if you chain your bike to nothing but itself...

if you chain your bike to nothing but itself, then you might be a security idiot.

if you use a wire chain that can be easily broken with pliers, chances are exceptionally good that you're a security idiot.

and if you do all that not five feet from a bus stop where a thief can make a speedy getaway without even removing the chain, then you're definitely a security idiot.

(inspired by my morning commute to work)

mobile computing and shoulder surfing

from here

mobile computing gives people the ability to access computing resources wherever they go. unfortunately, human nature is such that people go where there are other people. it's difficult to maintain the operational security necessary to even do something as simple as enter a password when you're in a public place surrounded by other people.

and infosec professionals think the only problem with the consumerization of IT is locking down the device (or the data on it)? ha! are they ever in for a surprise.

Tuesday, January 24, 2012

WTF anonymous?

from here

are you like me, folks? did anonymous' retaliation for the megaupload takedown make you scratch your head and wonder what the heck they were thinking? it's not like the takedown harms filesharing at all, since file locker sites are a dime a dozen (heck, even google docs is a file locker of sorts). the takedown really seems to do more to harm the interests of SOPA/PIPA supporters than anything else, since taking down a foreign website and making arrests overseas highlights just how much of an unnecessary power-grab those proposed bills really were.

as some were suggesting on twitter, it seems like they're trying to snatch defeat from the jaws of success.